Cyberattacks on South Korean Megachurches Expose Member Data
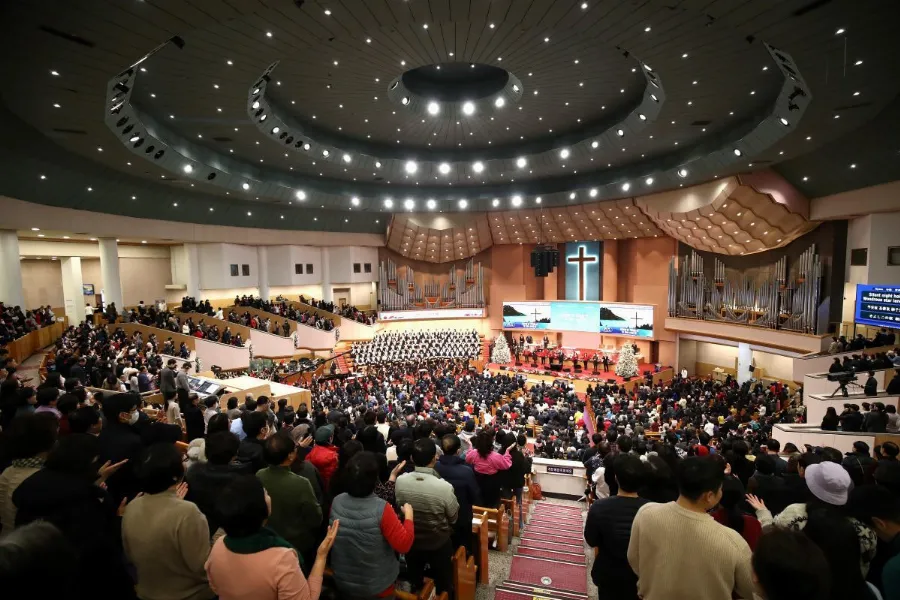
Two prominent South Korean megachurches, Yoido Full Gospel Church and SaRang Church, have reported a significant data breach involving the personal information of their congregants. Security firm Oasis Security identified attack records on an overseas server, suggesting that the personal data of approximately 850,000 members from Yoido Full Gospel Church may have been compromised. The exposed information includes names and birth dates, with some records containing phone numbers, addresses, and national identification numbers.
Senior Pastor Lee Young-hoon of Yoido Full Gospel Church issued a formal apology, expressing deep responsibility for the incident. The church is currently collaborating with the Korea Internet & Security Agency and cybersecurity experts to investigate the breach and prevent further unauthorized access. Measures taken include blocking external system access, updating server passwords, and notifying affected individuals. The church also plans to implement enhanced firewall protections and engage security firms to identify further vulnerabilities.
Reports from Oasis Security indicate that the hackers may have utilized artificial intelligence tools, including automated sub-agents, to facilitate the intrusion. While the specific role of AI in the attack remains under investigation, the church has confirmed that thousands of membership entries were modified during the breach.